95 lookalike download sites, and the one that served malware
A Rust player looks for Rust Tweaker, a tool that tunes the game's
settings, and lands on rusttweaker[.]org. The Download button gives a
small zip with a README. The README links to a 226 MB archive. Its
install.exe asks for administrator rights every second
until the user says yes, adds its folder to Microsoft Defender's
exclusions, then decrypts and runs a Windows payload.
rusttweaker[.]org is one of 95 lookalike download sites run from one hosting reseller. Almost every other Download button leads to the real file of the tool the site copies. The payload on this one was hidden as 440,336 English words, one word per byte.
Where it started
The hunt for lookalike domains aimed at tech workers listed burpsuite[.]org as a fake Burp Suite site and left its download "not analysed". This post closes that point. The certificate of burpsuite[.]org led to 94 more domains, and every download they offer was checked. Nothing was executed.
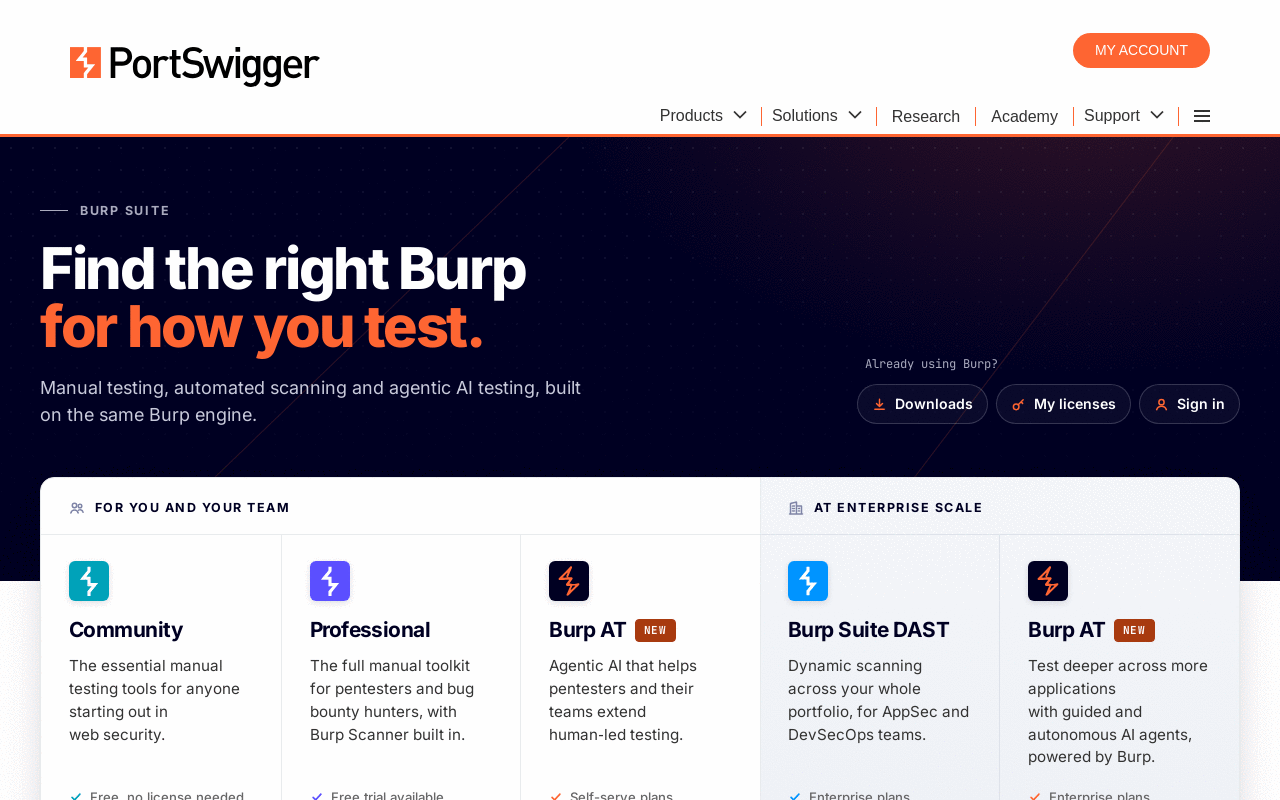 real: portswigger.net
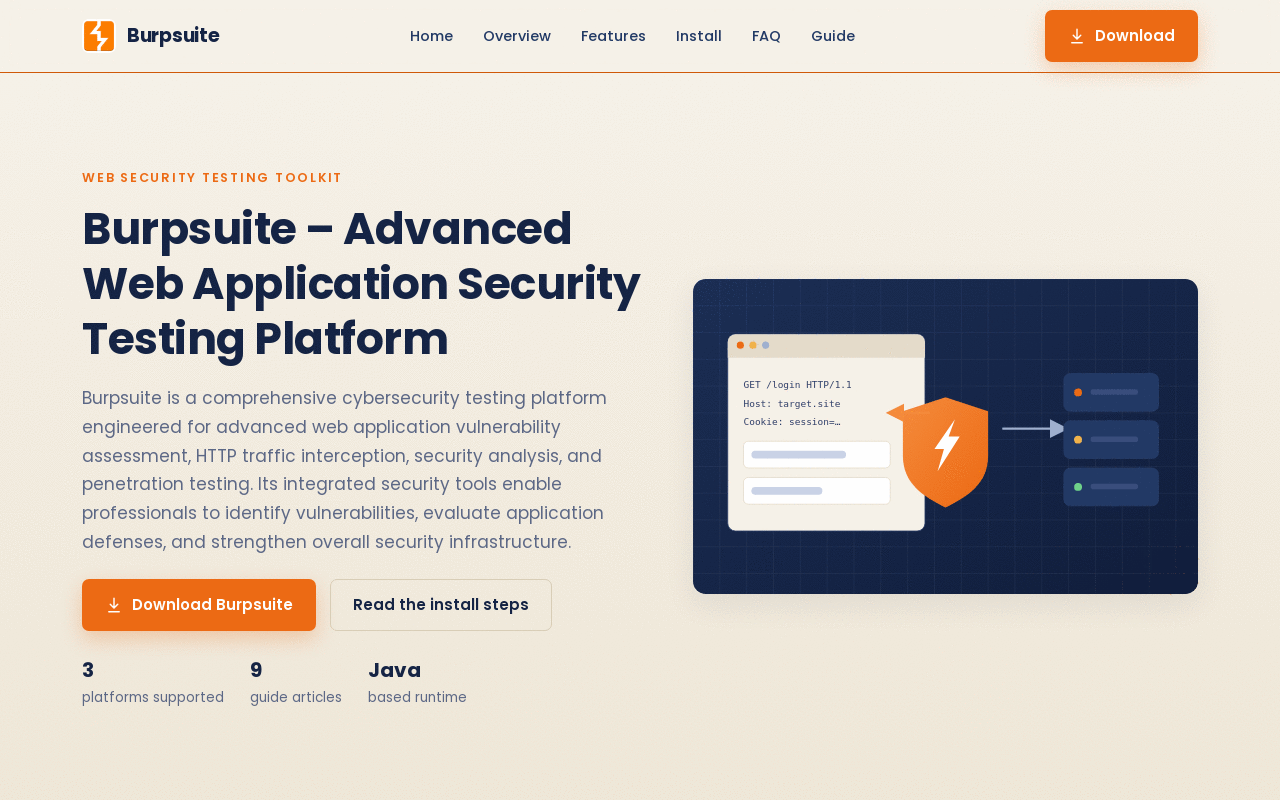 farm: burpsuite[.]org
How the farm was mapped
The site is not behind Cloudflare. It sits on 45.82.67.241, a shared
server of Middlehost, a hosting
reseller based in Karachi, Pakistan. Its Let's Encrypt certificate
lists 20 names, and some look broken:
www.burpsuite.org.angryipscanner.org.
They are not broken. cPanel, the control panel of most shared hosts, lets one account hold several sites. Each extra site, an "addon domain", gets an internal name made of the site plus the account's main domain. AutoSSL, cPanel's free certificate service, then puts those names on the certificate. So the certificate says which sites share an account, and which domain owns it.
- Read the certificate a site serves.
-
Split every
<addon>.<primary>name into two domains. - Resolve each new domain, read its certificate, and repeat until no new name appears.
- Add a sweep of the daily new-domain lists from 1 to 17 November for names served by Middlehost's nameservers, to catch sites that are alone on their account.
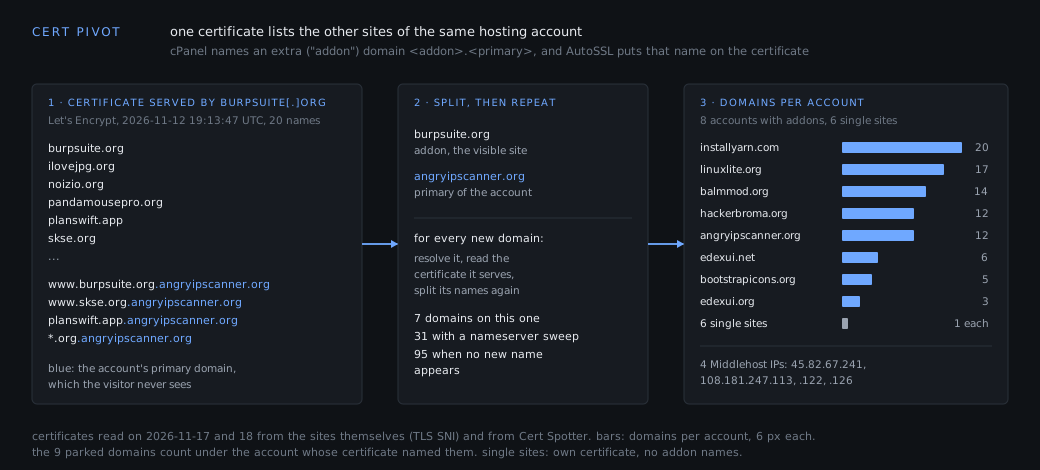
The loop stopped at 95 domains: 8 cPanel accounts with addon domains and 6 sites alone on their own certificate. The same trick works on cPanel hosts whose AutoSSL certificates carry the addon names, and Cert Spotter or crt.sh give the older certificates of a domain.
What the farm is
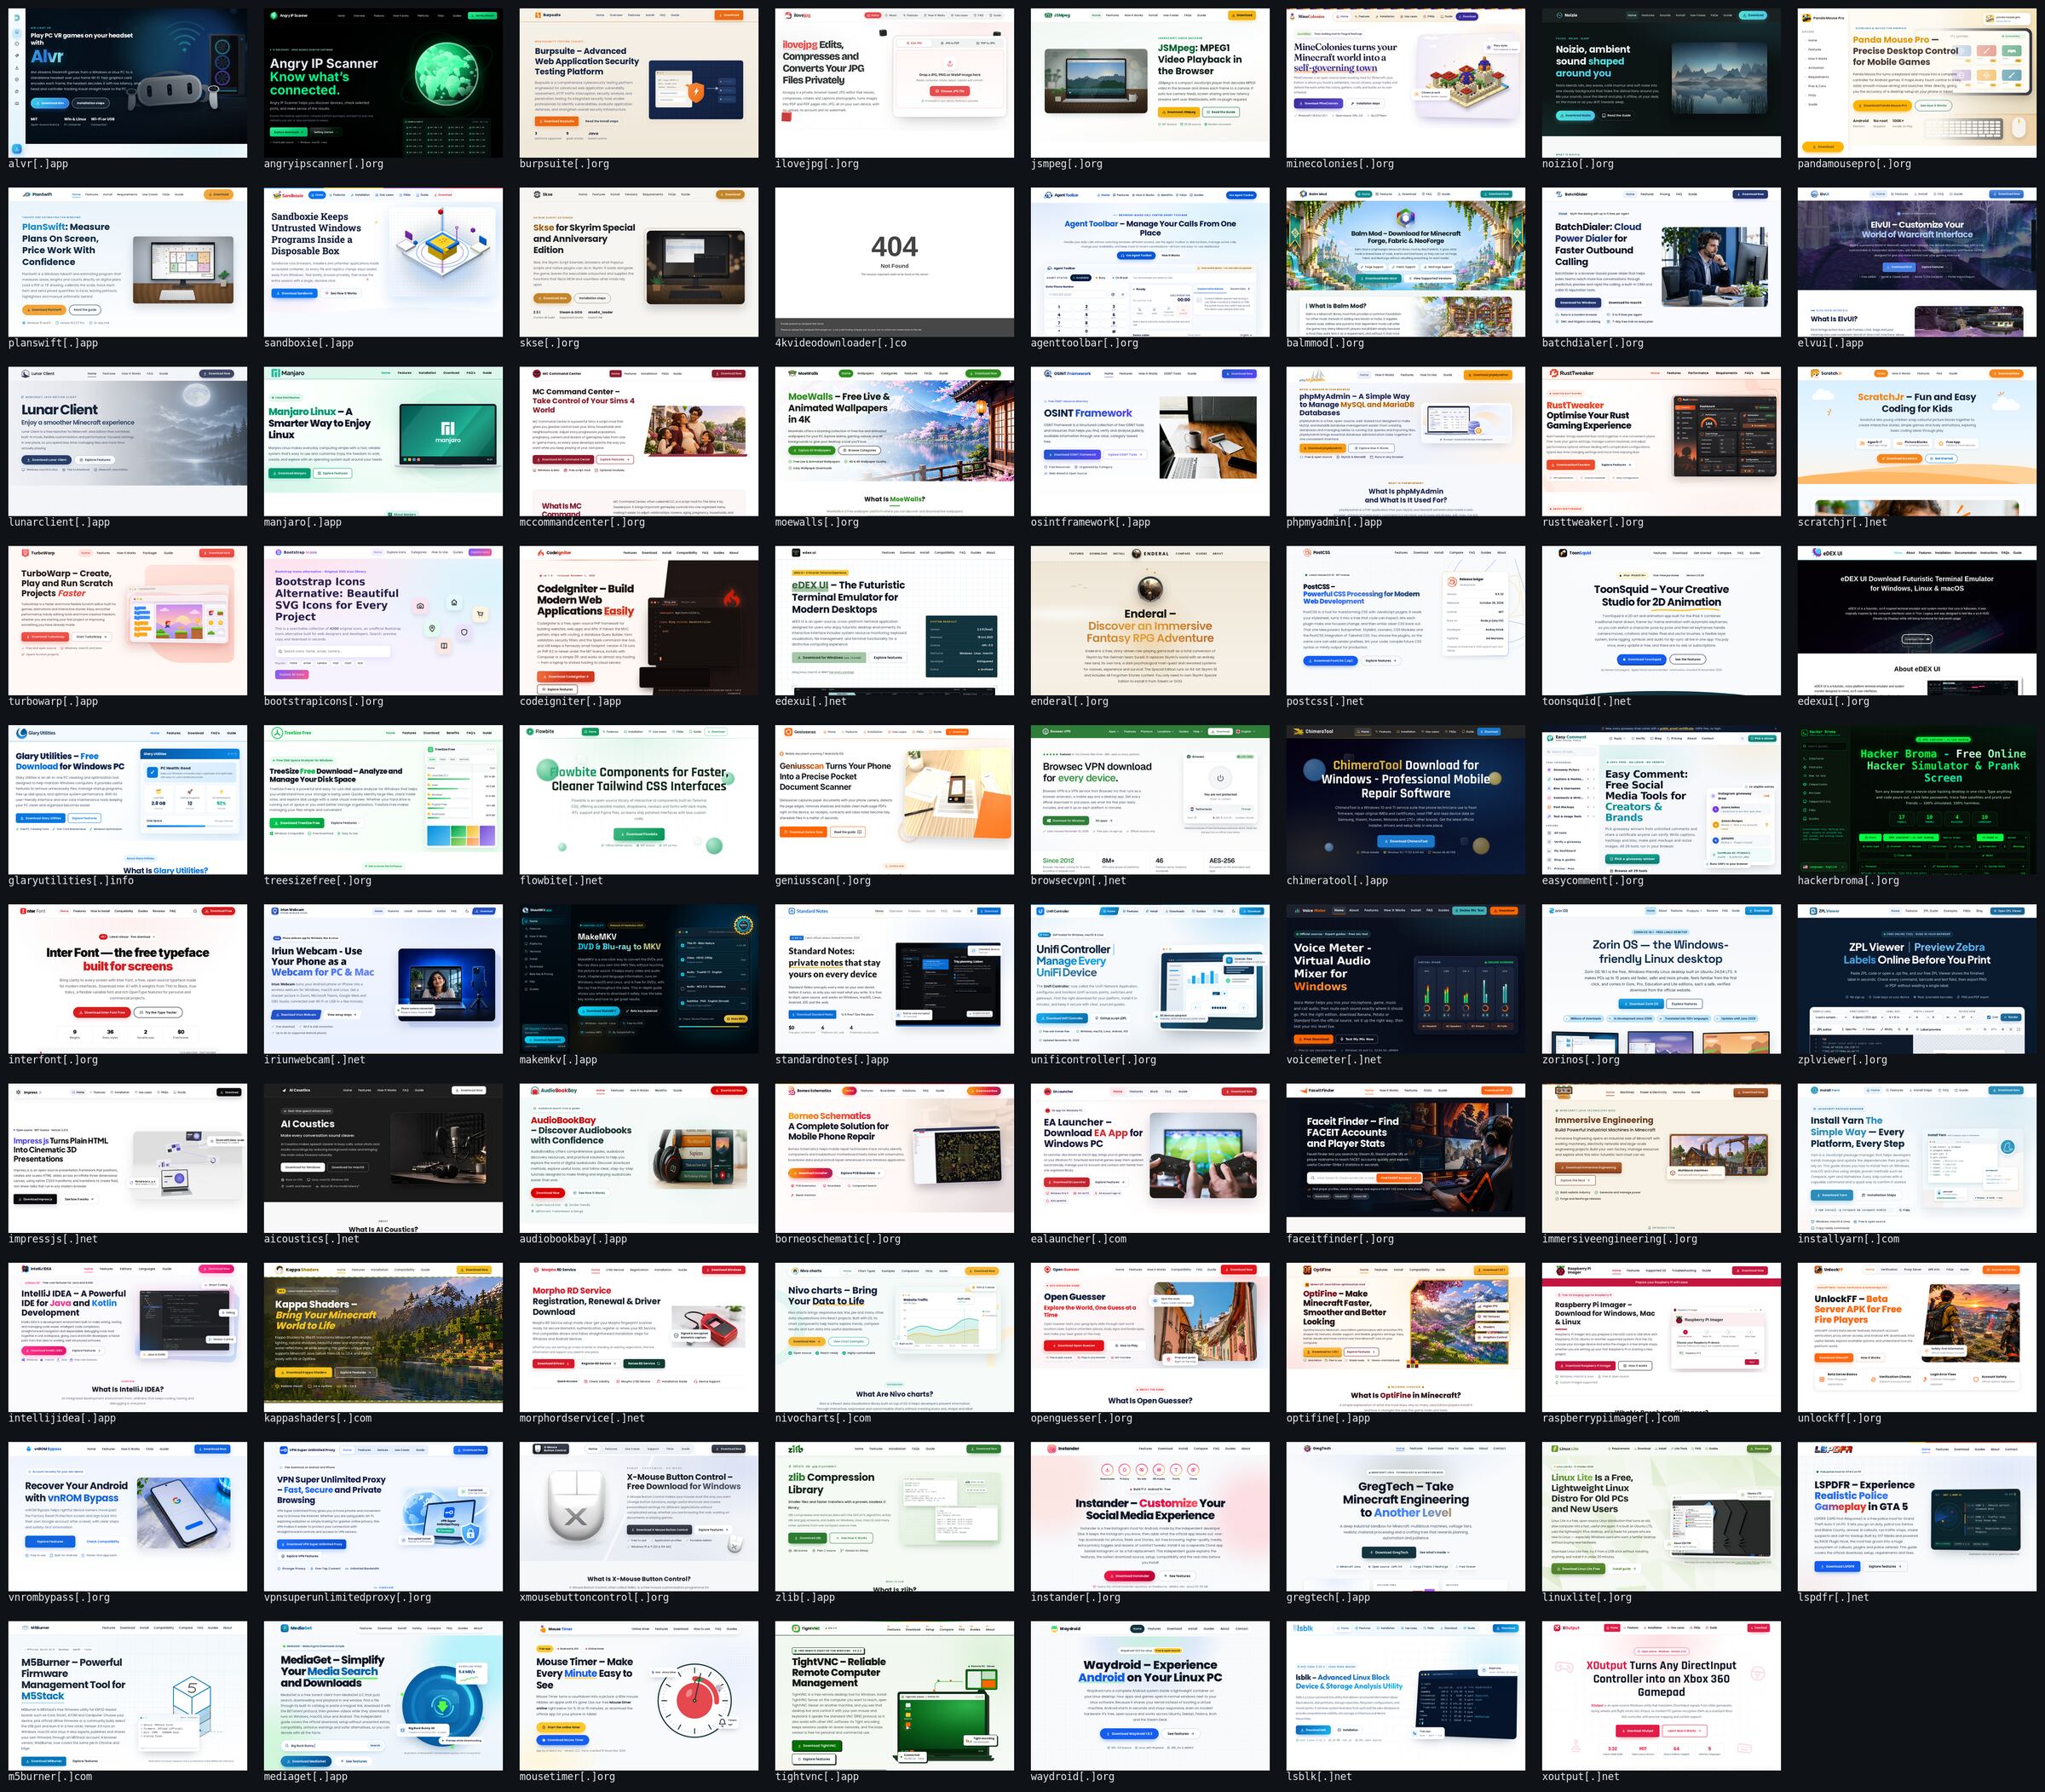
- 95 domains. 79 serve a page, 5 an empty directory listing, 2 an error, and 9 point to a Team Internet parking server. 40 are .org, 28 .app, 16 .net, 9 .com.
- Bought in batches. 62 were registered on 3 November 2026 in four batches, at 11:59, 12:34, 12:46 and 13:17 UTC. Then 6 on 4 November, 19 on 7 November and 5 on 8 November. Most went through Dynadot, the nine .com names through Gransy in the same minutes. edexui[.]org came earlier, through Spaceship.
- Some names had a past. skse[.]org was for sale in 2019 and shown as expired at Spaceship in July 2025. burpsuite[.]org was a for-sale page in 2021. angryipscanner[.]org showed a copy of angryip.org in 2025. The Wayback Machine also has older lives for lspdfr[.]net, kwiky[.]net and jibble[.]app. An expired domain keeps its links and its place in search results.
- The brands are tools people install by hand. Security and IT: Burp Suite, Angry IP Scanner, Sandboxie, TightVNC, phpMyAdmin, OSINT Framework, UniFi Controller, TreeSize, Glary Utilities. Developer: IntelliJ IDEA, Git Bash, CodeIgniter, PostCSS, zlib. Games and mods: SKSE, LSPDFR, Lunar Client, OptiFine, MineColonies, a Roblox "executor". Phone repair and Android bypass tools.
- Static pages, a few WordPress. 5 sites run WordPress, the others are static HTML. The static code differs from site to site but repeats the same comments ("FAQ: only one answer open at a time"), as if generated from one prompt each time. The WordPress sites are signed by invented authors: "Edward Higgins", "Juliette Wu", "Brandon", "Leona".
- Built for search, not paid yet. 77 of the 79 sites have about-us, privacy, terms, disclaimer and contact pages, the set Google AdSense asks for. 19 carry a Google Search Console verification tag. No home page carries an ad, an analytics tag or an affiliate link.
- Older than November. edexui[.]org, the primary of one account, was registered on 16 March 2026 and holds WordPress posts and uploads dated 1 September 2025.
What the downloads are
Every sitemap page of the 95 domains was crawled for links to files, installers and download pages. Most buttons go to the vendor or to the project's GitHub. Ten sites host a file themselves. Each of those was checked against the original:
-
Byte-identical to upstream: the zips on
noizio[.]org, alvr[.]app, jsmpeg[.]org and edexui[.]org match the
GitHub archive of the same commit, file by file. The
Inter-4.1.zipon interfont[.]org has the same SHA-256 as the official release. - Valid vendor signature: planswift[.]app serves PlanSwift's own 2018 installer, Authenticode hash recomputed and matching. treesizefree[.]org serves Microsoft's signed Store web installer.
- Harmless: manjaro[.]app serves a copy of Manjaro's release-review repository. glaryutilities[.]info serves a README with no link.
- Malicious: rusttweaker[.]org. Details below.
The third-party links were checked too. burpsuite[.]org points to a cracked Burp Suite Pro on GitHub and Google Drive: the 533 MB archive holds PortSwigger's official 2024.7.5 JAR (same size and CRC32) and the open-source BurpLoaderKeygen. It was read with HTTP range requests, without downloading it whole. That is piracy, not a trojan. mccommandcenter[.]org links the author's own Google Drive file. Some picks are careless: "Download Panda Mouse Pro" gives the source code of a different Android project, an ADB client.
The one that serves malware
TL;DR, what the payload does (quick reverse of every layer with keys found in the layer above):
-
install.exe(79.6 MB) unpacks an Electron app whosemain.js(5 MB) is obfuscated. The loader:- quits on virtual machines and sandboxes (it checks CPU, RAM, uptime, GPU, fans and machine names);
- asks for admin rights every second until the user accepts;
-
adds its drop folder under
%LOCALAPPDATA%and its own program to Microsoft Defender's exclusions; - decrypts a payload hidden after the end of a PNG image (AES-256-CBC) and runs it.
-
That payload,
gyhmlGIZJ.exe, is signed with a self-made certificate ("ColdGlen Ridge Ltd."). It stores the next file as 440,336 English words, one word per byte, then decrypts it with AES-256-CTR. - The result is a 440 KB 64-bit Windows program with no readable strings. Family not identified; that would take a full reverse-engineering session.
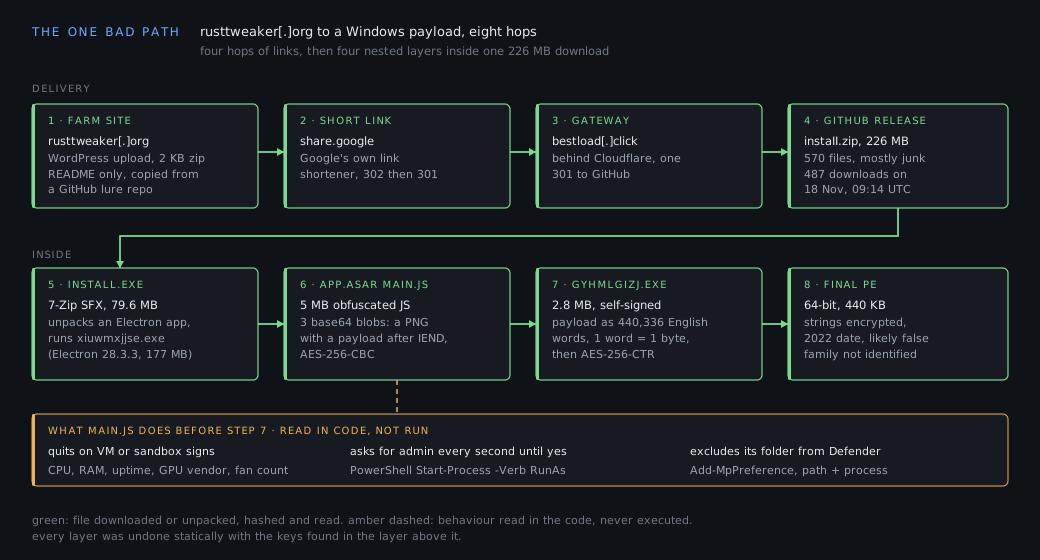
1. The farm site and the redirect
rusttweaker[.]org runs WordPress. Its home page was created on 9
November at 18:03 (site time), and the zip behind the Download button
was uploaded 30 minutes later. The zip holds one README, a copy of the
GitHub repository
Restraintnovapurify/Rust-Tweaker-Config-Architect. Its
owner account and the repository were created on 21 June 2026, three
minutes apart.
The README follows a template common to fake GitHub "download" repos:
a big "DOWNLOAD, Click here" link, a Setup.exe to run, a
"Legality" paragraph and a tag list. The link goes to
share.google/JEV5AnVe5tQ1NYwgT, Google's own link
shortener, then to bestload[.]click, then to a GitHub release:
https://share.google/JEV5AnVe5tQ1NYwgT                      302
https://www.google.com/share.google?q=JEV5AnVe5tQ1NYwgT     301
https://bestload.click/                                     301
https://github.com/MarkVeteranFight/app2/releases/download/ert3t3/instaII.zip
The GitHub account was created on 15 August 2026. The release dates from 10 November, and its asset was replaced on 17 November at 10:09 UTC. It counted 438 downloads at 06:31 UTC on 18 November and 487 at 09:14 UTC. After the farm site, every hop but the gateway is a large platform people trust. The gateway is the one domain to block.
2. instaII.zip and install.exe
The name uses capital I's to read as "install". The 226 MB zip holds
570 files. Most are padding: random bytes (entropy 8.00) named
source_127.yaml or stats_222.cob, spread
over folders that also hold a Qt plugin and the modules of a Browser
Automation Studio project. A file this big is often skipped by
sandboxes and upload-based scanners.
The real file is install.exe, 79.6 MB, dated 17 November
10:33 in the zip. It is a stock 7-Zip 25.01 self-extractor whose
configuration runs one program:
;!@Install@!UTF-8!
RunProgram="xiuwmxjjse.exe"
GUIMode="2"
The archive unpacks an Electron app: xiuwmxjjse.exe (177
MB, Electron 28.3.3's stock version information) and
resources/app.asar. The logic sits in
main.js inside the asar, 5 MB on a single line.
3. main.js, the loader
Every string is pulled from a table of 615 encoded entries. The decoder rotates the table 235 times, then applies base64 with a custom alphabet, RC4 with a per-call key, and UTF-8. Reimplemented in Python, it replaces the 1,272 calls and leaves 629 readable lines. In order, the script:
- Quits on analysis machines. It leaves at once on anything but Windows, on 1 CPU, or on a QEMU, KVM or hypervisor CPU name. It then scores the machine: uptime under 3 or 15 minutes, under 2 GB of RAM, 2 CPUs, a host or user name containing "sandbox", "malware", "cuckoo" and the like, and a PowerShell inventory of GPUs, fans, thermal zones, memory slots and ports. Virtual GPU vendors (VMware, VirtualBox, QEMU, Hyper-V) end the run. A score of 6 does too.
-
Nags for admin rights. It checks whether it runs
elevated. If not, it relaunches itself with
Start-Process -Verb RunAs, once a second, until the user accepts the prompt. -
Blinds Defender. Three
Add-MpPreferencecalls exclude its drop folder, every process in it, and its own executable. -
Drops the next stage. It joins three base64 blobs
into one 2.8 MB buffer. The first 48,977 bytes are a valid 152 by
107 PNG. Everything after the PNG's
IENDchunk is AES-256-CBC with a key and IV written in the script. The result is written asgyhmlGIZJ.exein%LOCALAPPDATA%\HoBnbIU\qyOFEkwt\iphKq\jxFuMJZD\and started detached.
// the PNG ends with IEND + CRC; the payload follows
const marker = Buffer.from([0,0,0,0,73,69,78,68,174,66,96,130]);
const body = blob.subarray(blob.lastIndexOf(marker) + marker.length);
const d = crypto.createDecipheriv("aes-256-cbc",
  Buffer.from("947904eca76ef3614c72861eec9e1cef9660a601e5b18fbc452202789db57851", "hex"),
  Buffer.from("4803b8e8d2f240adeca6131b8f2a98b9", "hex"));
fs.writeFileSync(path.join(dir, "gyhmlGIZJ.exe"), Buffer.concat([d.update(body), d.final()]));
Two features are present and switched off. A list of seven fake crash
messages ("MSVCP140.dll is missing", "0xc000007b") would be shown on
exit, but its flag is "0". A second loader that reads a
download URL from a Telegraph page
is never called, and its page name and keys are empty. The loader adds
no persistence.
4. gyhmlGIZJ.exe, the payload written in words
The dropped file is a 2.8 MB 64-bit program compiled on 17 November at 09:31 UTC. It poses as "Updater for Ping Target" by "ColdGlen Ridge Ltd., Inc.", with decoy settings, menus and status strings. Its signature is valid but self-signed: the certificate names itself as issuer, with a real DigiCert timestamp. Windows does not trust it.
Most of the file is text: 36,694 lines of exactly 12 words and one of 8, such as:
text | .rdata, first sentencesmany name user new than why when module from animal help three
about about had only animal if because do still there set run
good number help so paper animal letter is why land too library
The sentences use exactly 256 distinct words. A table of 256 pointers
at .rdata+0x6d0 gives each word its byte value. The
decoder at 0x140001000 splits the text on whitespace,
finds each word by a djb2 hash, and XORs the index with the repeating
key bb 4e b6 a4. That gives 440,336 bytes of noise. The
same function then builds an AES key from
.rdata+0x360 (each byte XORed with
7*i + 0x11) and a 12-byte nonce from
.rdata+0x380, and decrypts with AES-256 through Windows'
BCrypt API (its stack strings name AES and
ChainingModeECB), used as a counter mode with a
little-endian counter.
table = {word_at(p): i for i, p in enumerate(ptrs)}       # 256 words
key4  = bytes([0xbb, 0x4e, 0xb6, 0xa4])
out   = bytes(table[w] ^ key4[i % 4] for i, w in enumerate(text.split()))
aes_key = bytes(rdata[0x360 + i] ^ ((7*i + 0x11) & 0xff) for i in range(32))
nonce   = rdata[0x380:0x38c]                                # counter: nonce + LE32(i)
Words keep the file's entropy low, so a scanner that flags packed or
encrypted data sees plain English. The output starts with
MZ and is a valid program.
5. The final payload
A 64-bit executable of 440,336 bytes with a February 2022 timestamp,
probably false. Its imports are decoy GUI calls, and no readable
string remains. The disassembly shows AES-NI instructions, constants
that look like API name hashes, and CPUID and RDTSC instructions,
which anti-VM checks use but ordinary runtime code also does. The
family is not identified. A machine that ran
install.exe and accepted the admin prompt should be
treated as compromised.
Who is behind it, and why
No name. The evidence points to one operator:
- Same buyer: same registrar, same minutes, same hosting reseller, names chained through cPanel accounts.
-
Same maker: one page layout, one set of legal
pages, near-identical disclaimer wording ("not affiliated with,
endorsed by or sponsored by"), invented authors, a few Gmail
contacts built the same way (
support.ilovejpg,support.uikitdesk,hello.xoutputhelp,lsblkdesk).
The goal seen today is search traffic. Exact-match and expired domains, a "download" page for each tool, Search Console tags and AdSense-ready legal pages fit a farm that will sell ads or traffic once the pages rank. That is a reading of the setup, not an observation: no ad or tracking code was seen on any home page.
The malware is the exception, and its origin is narrow. The operator copied a GitHub lure repository as the "download" for one tool, the same way other sites copy a GitHub archive. Whether the operator knew is not known. The effect is the same for a visitor, and one operator controls the Download button of 95 sites: changing a link takes a minute.
Limits
- The sweep is a sample. The daily new-domain lists are capped at 70,000 names, and only .org, .app, .net, .io, .dev, .co and .cc were swept for Middlehost nameservers, plus .com on seven days. Sites alone on an account and not in that sample are missed.
- Pages were seen from one place. Windows, macOS, Android, Googlebot and search referrers got the same bytes on the four sites tested. Cloaking by country or by IP reputation was not tested.
- Downloads move. Each link was checked once, between 17 and 18 November. The GitHub asset had already been replaced once.
- The last stage is not analysed. Its strings, network traffic and family are not known. The loader's behaviour was read in code, never run.
- The parked domains are inferred. The 9 domains parked at Team Internet appear in the farm's certificates, but their pages were not seen.
What to do
- Treat a download portal as a third party. A site named after a tool is not the tool's site. Get IT and security tools from the vendor or the project's own GitHub releases.
- Check where the file comes from, not the page. A Download button that leads to a README, a short link or a fresh GitHub account is the sign, whatever the page looks like.
-
Read certificates during an investigation. Names
shaped like
site.tld.other.tldon a cPanel host list the rest of the account. -
Hunt for the loader's actions.
Add-MpPreferenceexclusions under%LOCALAPPDATA%, repeated UAC prompts from the same program, and an Electron app started from a temporary 7-Zip folder. - Report the chain. bestload[.]click and the GitHub release are the parts a takedown would break. The farm sites are a watch item: only one serves malware today.
Indicators of compromise
The farm's IP addresses are shared hosting with unrelated customers. Block the domains, not the IPs.
| Type | Value | Note |
|---|---|---|
| URL |
hxxps://rusttweaker[.]org/wp-content/uploads/2026/11/Rust-Tweaker-Config-Architect-main.zip
|
Farm download, README only |
| URL | hxxps://share[.]google/JEV5AnVe5tQ1NYwgT |
Short link in the README |
| Domain | bestload[.]click |
Gateway, Cloudflare |
| URL |
hxxps://github[.]com/MarkVeteranFight/app2/releases/download/ert3t3/instaII.zip
|
GitHub user id 317190020 |
| URL |
github[.]com/Restraintnovapurify/Rust-Tweaker-Config-Architect
|
Lure repo copied by the farm |
| SHA-256 |
ba5d19275943e734838681de95086abaf9b47906bbecc461d694b80a91702127
|
Rust-Tweaker-Config-Architect-main.zip |
| SHA-256 |
fc98272ffa0ebe39caf5cdba8fecc2180b5c84f6519607766b8e7fc1ea0bbe77
|
instaII.zip, 226,845,283 bytes |
| SHA-256 |
31942d0837ef8ec9366507dd7f0a65ba791ba7d55905f2d3b24b1a5f4bccaa2d
|
install.exe, 7-Zip SFX |
| SHA-256 |
a83eec2f6018ac144dc6bf9b1cc911e24495faab39e802591944c89ea0bc2013
|
resources/app.asar |
| SHA-256 |
ea4d0be038cb788845fe340c76e02c37552d071411342095454d87ebfc7c6c28
|
main.js, obfuscated loader |
| SHA-256 |
5813bbbffa5d07b4883bdbcfec3f35bb2049c31afce820fe1de1b40ddfd9c4e2
|
gyhmlGIZJ.exe, "ColdGlen Ridge", self-signed |
| SHA-256 |
11ed12f209b0cdbc6f44c59a16f80060ecf521497814c71e330c0ab54285d860
|
Final payload, decoded in memory by gyhmlGIZJ.exe |
| Path |
%LOCALAPPDATA%\HoBnbIU\qyOFEkwt\iphKq\jxFuMJZD\gyhmlGIZJ.exe
|
Drop path, excluded from Defender |
| Key |
947904eca76ef3614c72861eec9e1cef9660a601e5b18fbc452202789db57851, IV 4803b8e8d2f240adeca6131b8f2a98b9
|
AES-256-CBC, stage 3 |
| Key |
016c1780ffef71df5e38150701eb9c926785d0e3c7b25cd7597f5c19a733758d, nonce def8df03cdc8280776cd91b3
|
AES-256-CTR, stage 4 |
| Domain | the 95 domains in the inventory below | Farm, watch list |
| IP |
45.82.67.241, 108.181.247.113,
108.181.247.122, 108.181.247.126
|
Middlehost shared servers, context only |
Inventory: the 95 domains, their account and what their Download button gives
Seen on 17 and 18 November 2026. "Account" is the cPanel primary domain named in the certificates. "Upstream" means the vendor's site or the project's own repository.
| Domain | Account | Registered | Download |
|---|---|---|---|
alvr[.]app |
angryipscanner[.]org | 2026-11-07 | self-hosted, identical to upstream |
angryipscanner[.]org |
angryipscanner[.]org | 2026-11-07 | upstream site |
burpsuite[.]org |
angryipscanner[.]org | 2026-11-07 | cracked Burp Pro: official JAR + open-source keygen |
flowbite[.]net |
angryipscanner[.]org | 2026-11-07 | upstream GitHub |
ilovejpg[.]org |
angryipscanner[.]org | 2026-11-07 | no download link |
jsmpeg[.]org |
angryipscanner[.]org | 2026-11-07 | self-hosted, identical to upstream |
minecolonies[.]org |
angryipscanner[.]org | 2026-11-07 | upstream GitHub |
noizio[.]org |
angryipscanner[.]org | 2026-11-07 | self-hosted, identical to upstream |
pandamousepro[.]org |
angryipscanner[.]org | 2026-11-07 | GitHub archive of an unrelated project |
planswift[.]app |
angryipscanner[.]org | 2026-11-07 | self-hosted, PlanSwift-signed installer |
sandboxie[.]app |
angryipscanner[.]org | 2026-11-07 | upstream GitHub |
skse[.]org |
angryipscanner[.]org | 2026-11-07 | upstream GitHub |
4kvideodownloader[.]co |
balmmod[.]org | not published | upstream site |
agenttoolbar[.]org |
balmmod[.]org | 2026-11-03 | no download link |
balmmod[.]org |
balmmod[.]org | 2026-11-03 | upstream site |
batchdialer[.]org |
balmmod[.]org | 2026-11-03 | upstream site |
elvui[.]app |
balmmod[.]org | 2026-11-03 | upstream GitHub |
lunarclient[.]app |
balmmod[.]org | 2026-11-03 | upstream site |
manjaro[.]app |
balmmod[.]org | 2026-11-03 | self-hosted, copy of Manjaro release-review repo |
mccommandcenter[.]org |
balmmod[.]org | 2026-11-03 | author's own Google Drive file |
moewalls[.]org |
balmmod[.]org | 2026-11-03 | no download link |
osintframework[.]app |
balmmod[.]org | 2026-11-03 | upstream GitHub |
phpmyadmin[.]app |
balmmod[.]org | 2026-11-03 | upstream site |
rusttweaker[.]org |
balmmod[.]org | 2026-11-03 | malware: README to share.google, bestload[.]click, GitHub |
scratchjr[.]net |
balmmod[.]org | 2026-11-03 | upstream site, app store |
turbowarp[.]app |
balmmod[.]org | 2026-11-03 | upstream GitHub |
bootstrapicons[.]org |
bootstrapicons[.]org | 2026-11-08 | no download link |
gitbash[.]app |
bootstrapicons[.]org | 2026-11-08 | empty directory listing |
jibble[.]app |
bootstrapicons[.]org | 2026-11-08 | HTTP 403 |
krnlexecutor[.]app |
bootstrapicons[.]org | 2026-11-08 | empty directory listing |
rpcsx[.]app |
bootstrapicons[.]org | 2026-11-08 | empty directory listing |
codeigniter[.]app |
edexui[.]net | 2026-11-07 | upstream site, upstream GitHub |
edexui[.]net |
edexui[.]net | 2026-11-07 | upstream GitHub |
enderal[.]org |
edexui[.]net | 2026-11-07 | no download link |
instander[.]org |
edexui[.]net | 2026-11-07 | upstream site |
postcss[.]net |
edexui[.]net | 2026-11-07 | upstream GitHub |
toonsquid[.]net |
edexui[.]net | 2026-11-07 | app store |
edexui[.]org |
edexui[.]org | 2026-03-16 | self-hosted, identical to upstream |
glaryutilities[.]info |
edexui[.]org | not published | self-hosted, README without link |
treesizefree[.]org |
edexui[.]org | 2026-11-07 | self-hosted, Microsoft Store web installer |
geniusscan[.]org |
geniusscan[.]org | 2026-11-04 | app store |
browsecvpn[.]net |
hackerbroma[.]org | 2026-11-03 | upstream site, upstream GitHub |
chimeratool[.]app |
hackerbroma[.]org | 2026-11-03 | upstream site |
easycomment[.]org |
hackerbroma[.]org | 2026-11-03 | no download link |
hackerbroma[.]org |
hackerbroma[.]org | 2026-11-03 | no download link |
interfont[.]org |
hackerbroma[.]org | 2026-11-03 | self-hosted, official Inter 4.1 zip |
iriunwebcam[.]net |
hackerbroma[.]org | 2026-11-03 | upstream site, app store |
makemkv[.]app |
hackerbroma[.]org | 2026-11-03 | upstream site |
standardnotes[.]app |
hackerbroma[.]org | 2026-11-03 | upstream site, upstream GitHub |
unificontroller[.]org |
hackerbroma[.]org | 2026-11-03 | vendor site, plus a third-party install gist |
voicemeter[.]net |
hackerbroma[.]org | 2026-11-03 | upstream site |
zorinos[.]org |
hackerbroma[.]org | 2026-11-03 | upstream site |
zplviewer[.]org |
hackerbroma[.]org | 2026-11-03 | no download link |
highcharts[.]app |
highcharts[.]app | 2026-11-04 | empty directory listing |
impressjs[.]net |
impressjs[.]net | 2026-11-04 | upstream GitHub |
aeroinstagram[.]com |
installyarn[.]com | 2026-11-03 | HTTP 404 |
aicoustics[.]net |
installyarn[.]com | 2026-11-03 | upstream site |
audiobookbay[.]app |
installyarn[.]com | 2026-11-03 | upstream GitHub |
borneoschematic[.]org |
installyarn[.]com | 2026-11-03 | MediaFire installer, not checked |
ealauncher[.]com |
installyarn[.]com | 2026-11-03 | upstream site |
faceitfinder[.]org |
installyarn[.]com | 2026-11-03 | upstream GitHub |
immersiveengineering[.]org |
installyarn[.]com | 2026-11-03 | upstream site |
installyarn[.]com |
installyarn[.]com | 2026-11-03 | upstream GitHub |
intellijidea[.]app |
installyarn[.]com | 2026-11-03 | upstream site |
kappashaders[.]com |
installyarn[.]com | 2026-11-03 | upstream GitHub |
morphordservice[.]net |
installyarn[.]com | 2026-11-03 | upstream site |
nivocharts[.]com |
installyarn[.]com | 2026-11-03 | upstream GitHub |
openguesser[.]org |
installyarn[.]com | 2026-11-03 | upstream GitHub |
optifine[.]app |
installyarn[.]com | 2026-11-03 | upstream site |
raspberrypiimager[.]com |
installyarn[.]com | 2026-11-03 | upstream site, upstream GitHub |
unlockff[.]org |
installyarn[.]com | 2026-11-03 | APKPure XAPK of a Play Store app, not checked |
vnrombypass[.]org |
installyarn[.]com | 2026-11-03 | APK on apktodo, third party, not checked |
vpnsuperunlimitedproxy[.]org |
installyarn[.]com | 2026-11-03 | App Store, APKPure XAPK, not checked |
xmousebuttoncontrol[.]org |
installyarn[.]com | 2026-11-03 | upstream site |
zlib[.]app |
installyarn[.]com | 2026-11-03 | upstream GitHub |
kwiky[.]net |
kwiky[.]net | 2026-11-04 | empty directory listing |
chitubox[.]app |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
cristaldiskinfo[.]com |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
gachaeditx[.]com |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
gregtech[.]app |
linuxlite[.]org | 2026-11-03 | no download link |
linuxlite[.]org |
linuxlite[.]org | 2026-11-03 | guide page, no download link |
lspdfr[.]net |
linuxlite[.]org | 2026-11-03 | download.it link, expired token |
m5burner[.]com |
linuxlite[.]org | 2026-11-03 | vendor CDN, plus a GitHub mirror |
mediaget[.]app |
linuxlite[.]org | 2026-11-03 | upstream site |
momentjs[.]org |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
mousetimer[.]org |
linuxlite[.]org | 2026-11-03 | app store |
prime95[.]org |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
pyautogui[.]net |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
superantispyware[.]app |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
terragrunt[.]app |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
tightvnc[.]app |
linuxlite[.]org | 2026-11-03 | GitHub mirror (not the vendor) |
truenasscale[.]org |
linuxlite[.]org | 2026-11-03 | parked, page not seen |
waydroid[.]org |
linuxlite[.]org | 2026-11-03 | upstream GitHub |
lsblk[.]net |
lsblk[.]net | 2026-11-04 | upstream site |
xoutput[.]net |
xoutput[.]net | 2026-11-04 | upstream GitHub |